
How it actually works
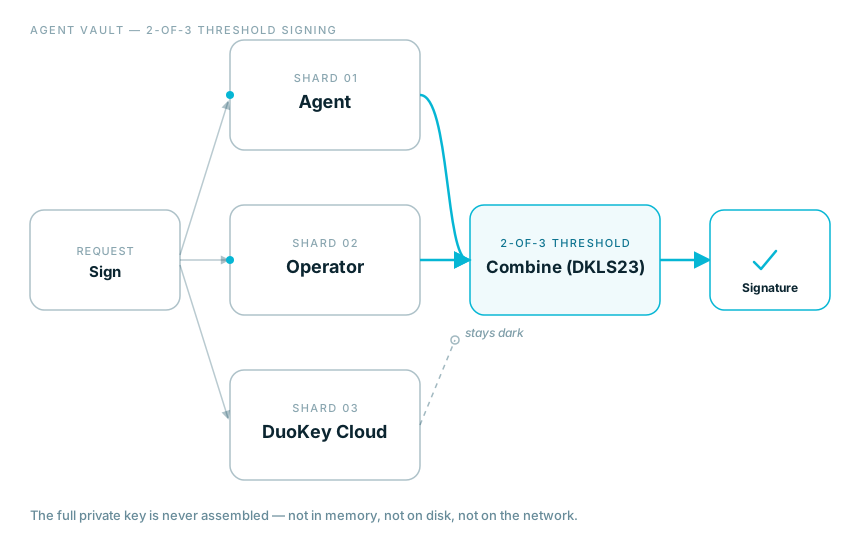
2-of-3 threshold signing: the full key is never assembled
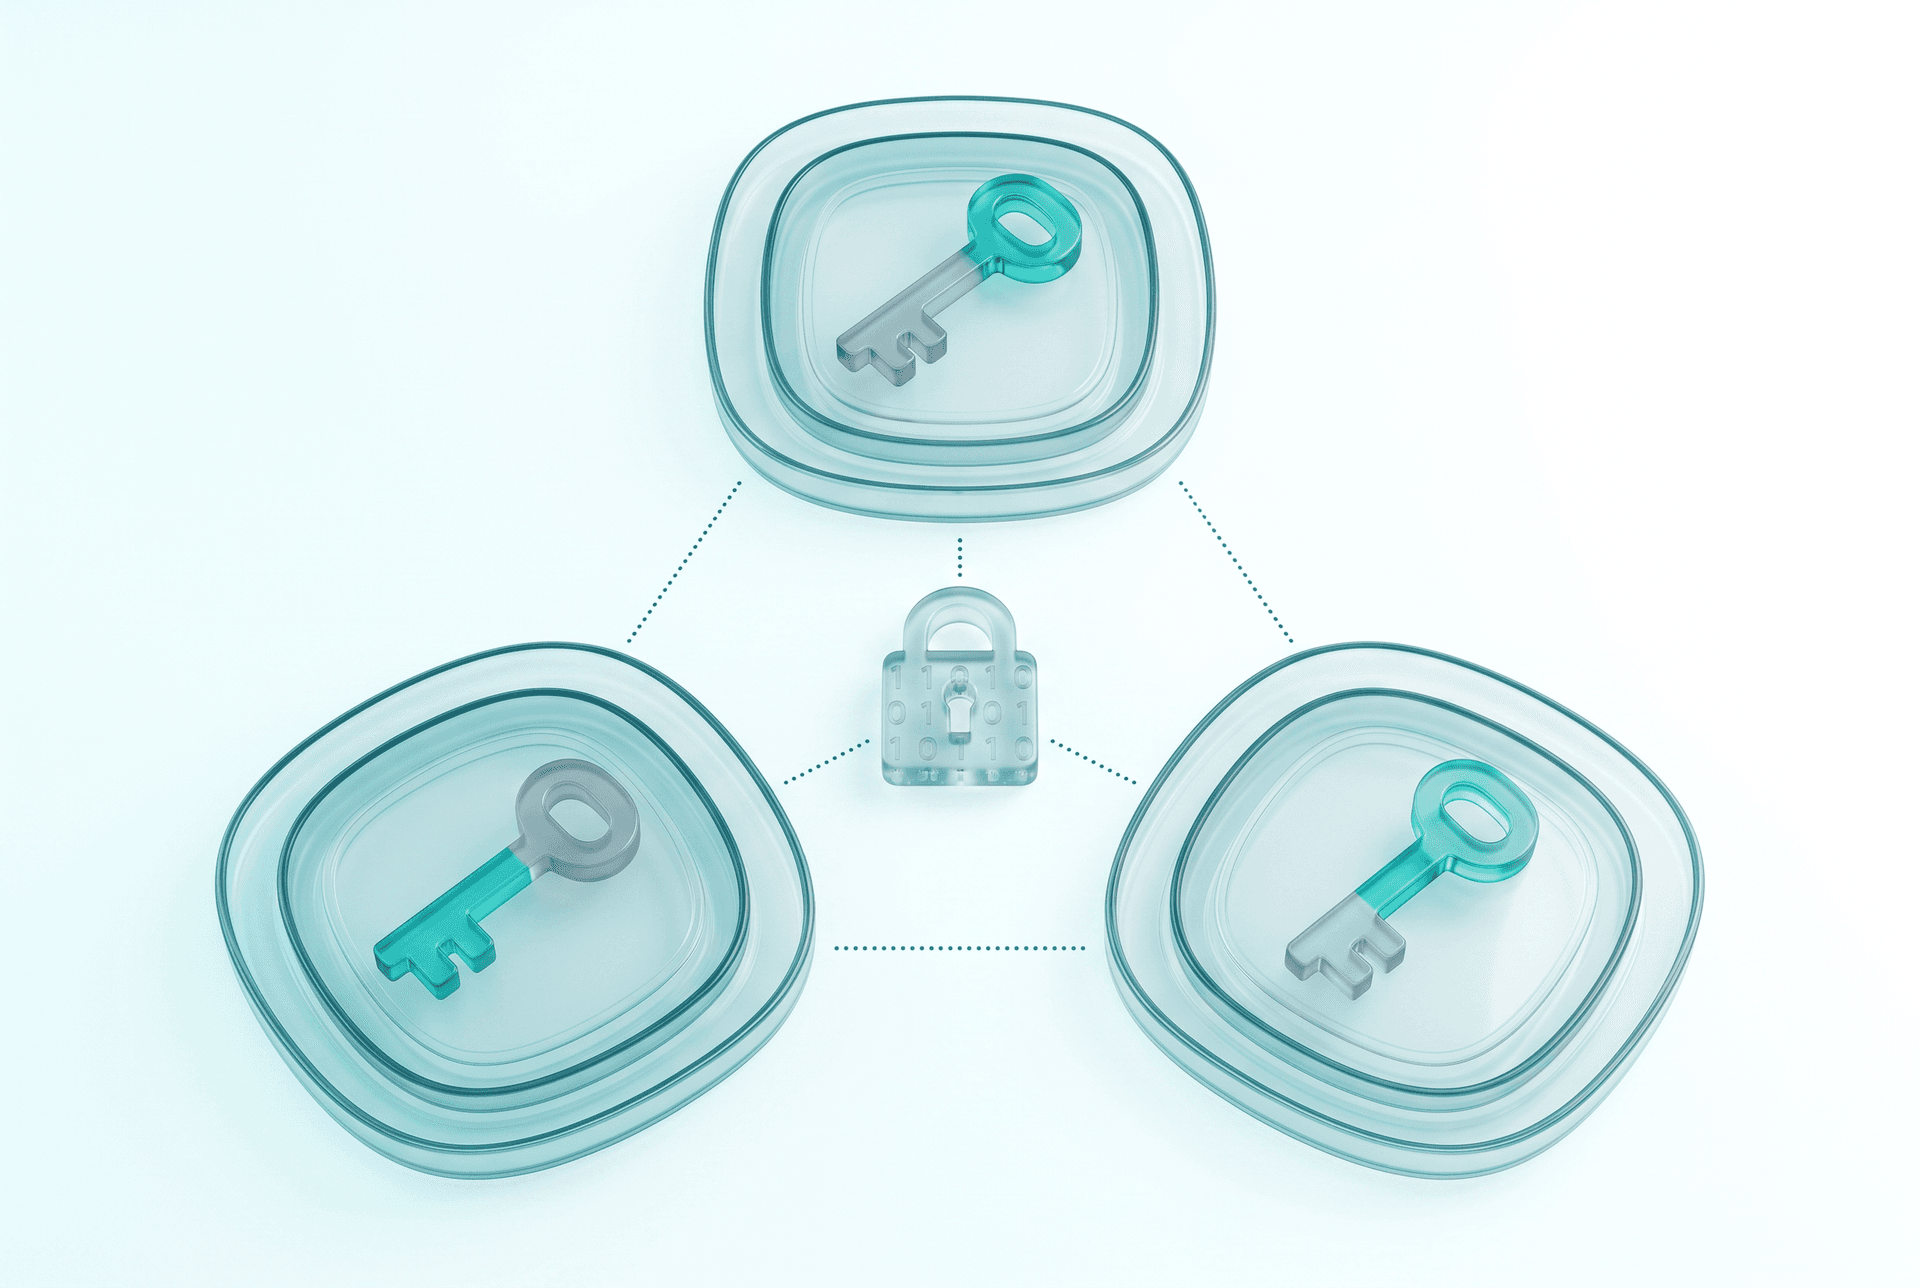
A sign request reaches all key shards at once, but only two need to respond to produce a valid signature. No shard, agent, operator or cloud provider ever holds enough of the key to act alone, and the combine step never reconstructs the full private key in memory, on disk, or on the network. Steal one shard and you have nothing usable.
- No single point of compromise: one stolen shard cannot produce a valid signature
- No HSM hardware to rack, patch, renew or run out of capacity
- Works the same way whether the shards sit in one cloud or three
- Every signature traceable to a named requester, not a shared service credential
Das Cockpit
Jeder Schlüssel, nach Algorithmus und Status markiert
Aktiv, deaktiviert oder kompromittiert: jeder Schlüssel über alle Vaults, mit klar ausgewiesenem Algorithmus, nicht in Metadaten versteckt.

Key generation
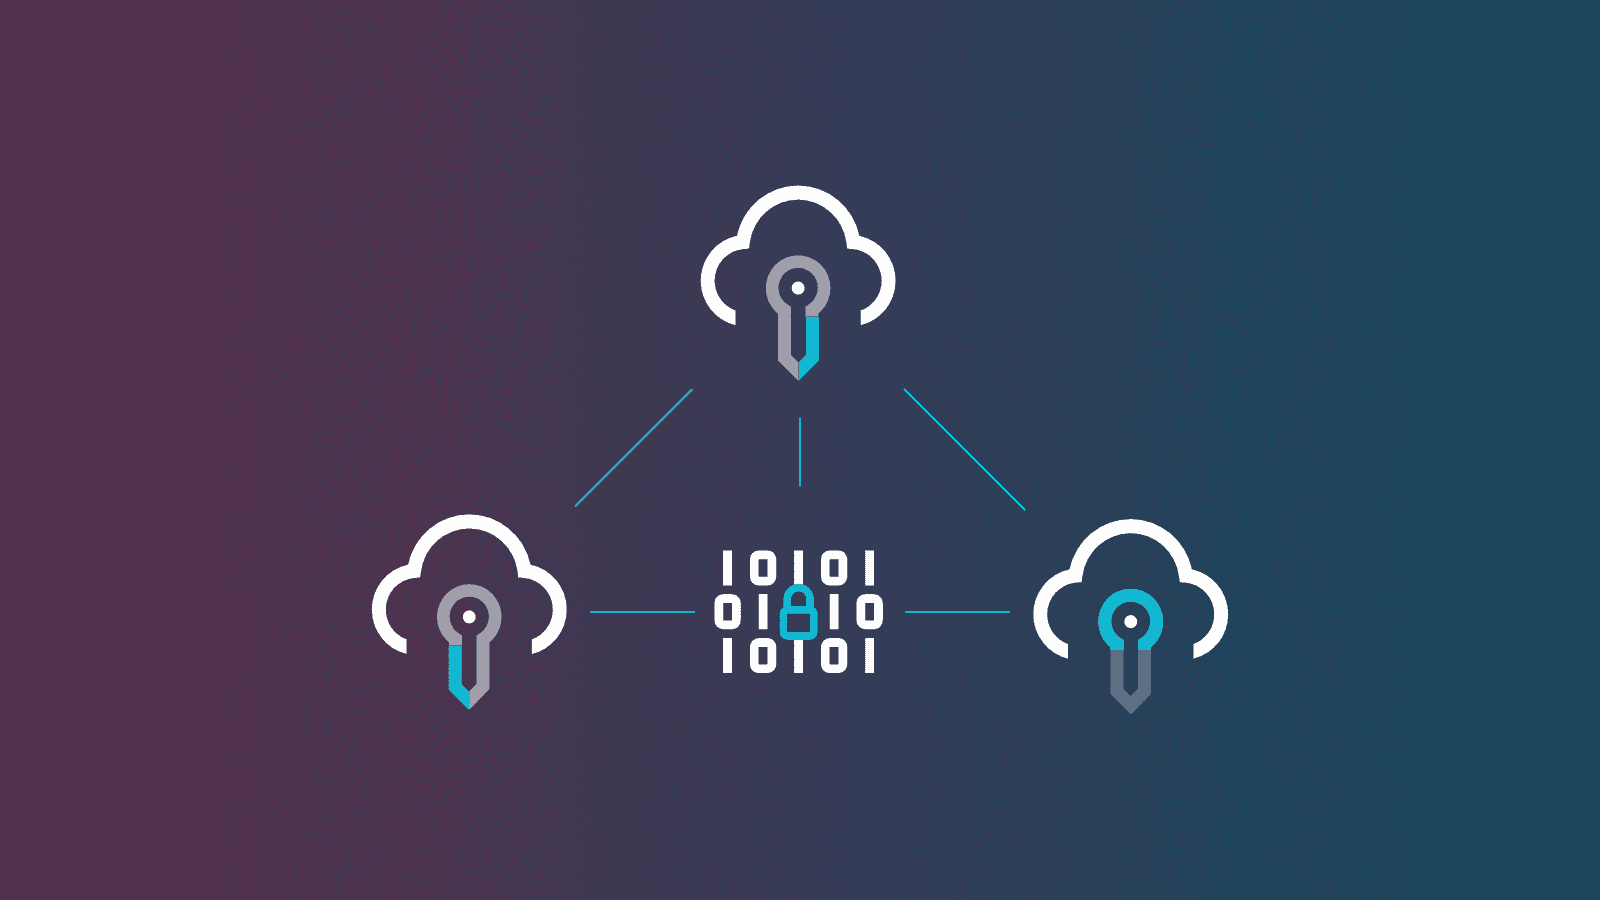
The key never exists whole, not even at birth
Generation is distributed the same way signing is: independent parties compute their own shard, and no single party, including DuoKey, ever observes the assembled private key. Rotation and revocation replace shards without ever reconstituting the key they protect.
Praxisbeispiele
Wo Teams das einsetzen
Tiefenanalysen
Leitfäden für Ihr Programm
Engagement
Stop trusting the cloud vault as the final word on keys
See the threshold signing model in your own environment, with keys that are never assembled, on any side.
Request a demoSprechen Sie über die Entscheidungen, die für Ihr Sicherheitsprogramm zählen.
Sagen Sie uns, wo Kontrolle heute schwierig ist. Wir helfen Ihnen, den nächsten praktischen Schritt zu finden.