
The problem
Key volume outruns the systems meant to govern it
More encrypted data means more keys, environments and regulatory overlays.
As estates scale, KMS fleets fragment across clouds, regions and applications. The result is operational overhead, inconsistent policy and no single answer to who can unwrap what.
A KMS per system
Each new app stands up another island of keys.
Dev / test / prod drift
Policy is rewritten in each environment.
Conflicting regimes
Each jurisdiction wants a different custody story.
Rotation backlog
Reviews cannot keep up with key volume.
How it actually works
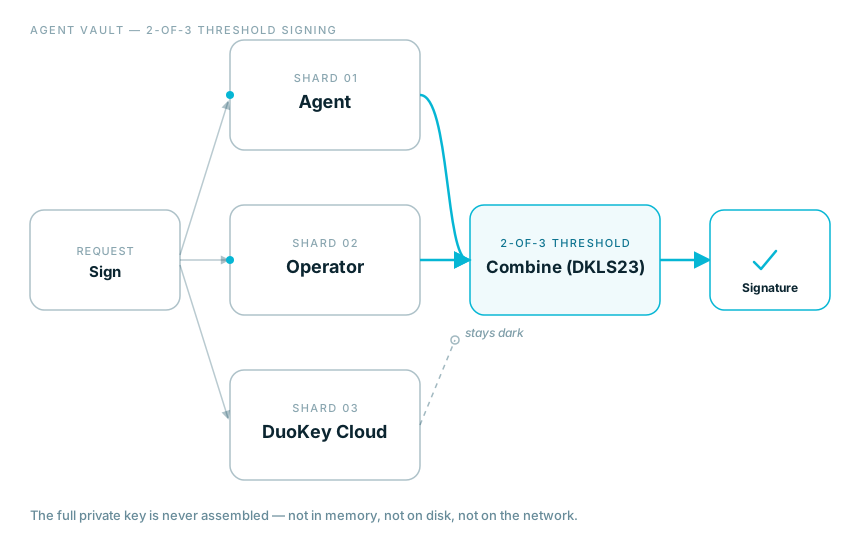
2-of-3 threshold signing: the full key is never assembled
A sign request reaches all key shards at once, but only two need to respond to produce a valid signature. No shard, agent, operator or cloud provider ever holds enough of the key to act alone, and the combine step never reconstructs the full private key in memory, on disk, or on the network. Steal one shard and you have nothing usable.
- No single point of compromise: one stolen shard cannot produce a valid signature
- No HSM hardware to rack, patch, renew or run out of capacity
- Works the same way whether the shards sit in one cloud or three
- Every signature traceable to a named requester, not a shared service credential
The Cockpit
Every key, tagged by algorithm and status
Active, disabled, or compromised, every key across every vault, with its algorithm called out, not buried in metadata.

Key generation
The key never exists whole, not even at birth
Generation is distributed the same way signing is: independent parties compute their own shard, and no single party, including DuoKey, ever observes the assembled private key. Rotation and revocation replace shards without ever reconstituting the key they protect.
Proof in practice
Where teams deploy this
Engagement
Stop trusting the cloud vault as the final word on keys
See the threshold signing model in your own environment, with keys that are never assembled, on any side.
Request a demoDiscuss the decisions that matter most to your security programme.
Tell us where control is difficult today. We will help you identify a practical next step.