
How it actually works
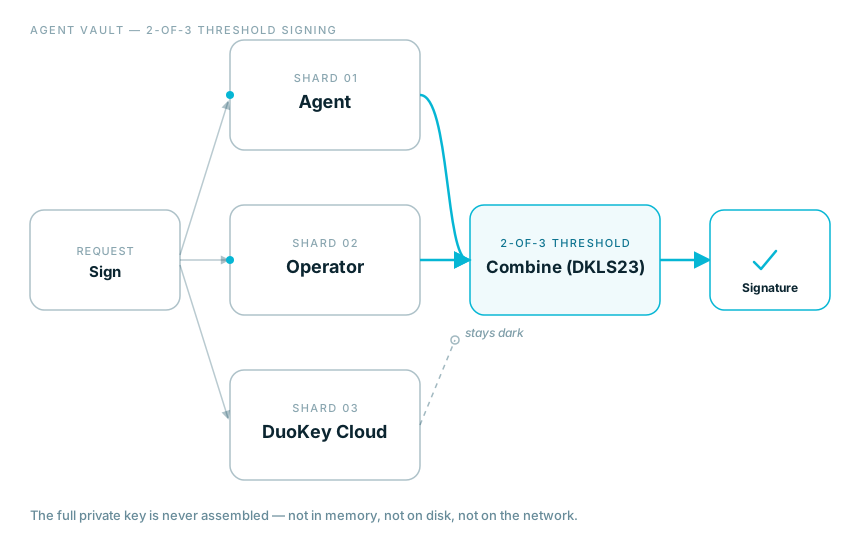
2-of-3 threshold signing: the full key is never assembled
A sign request reaches all key shards at once, but only two need to respond to produce a valid signature. No shard, agent, operator or cloud provider ever holds enough of the key to act alone, and the combine step never reconstructs the full private key in memory, on disk, or on the network. Steal one shard and you have nothing usable.
- No single point of compromise: one stolen shard cannot produce a valid signature
- No HSM hardware to rack, patch, renew or run out of capacity
- Works the same way whether the shards sit in one cloud or three
- Every signature traceable to a named requester, not a shared service credential
Le Cockpit
Chaque clé, taguée par algorithme et statut
Active, désactivée ou compromise : chaque clé de chaque vault, avec son algorithme clairement affiché, pas noyé dans les métadonnées.

Key generation
The key never exists whole, not even at birth
Generation is distributed the same way signing is: independent parties compute their own shard, and no single party, including DuoKey, ever observes the assembled private key. Rotation and revocation replace shards without ever reconstituting the key they protect.
Preuves terrain
Où les équipes déploient
Analyses
Guides pour votre programme
Engagement
Stop trusting the cloud vault as the final word on keys
See the threshold signing model in your own environment, with keys that are never assembled, on any side.
Request a demoParlons des décisions qui comptent pour votre programme de sécurité.
Dites-nous où le contrôle est difficile aujourd’hui. Nous vous aiderons à définir une prochaine étape concrète.