Citizens write to their administration what they share nowhere else: illnesses, debts, family situations. Staff forward files, offices coordinate. The mailbox is therefore an administration's largest and least ordered archive. With openDesk and OX App Suite, many administrations are bringing their email back from US clouds, often run by a public IT provider. The question remains: who can read these mailboxes?
Where the keys are today
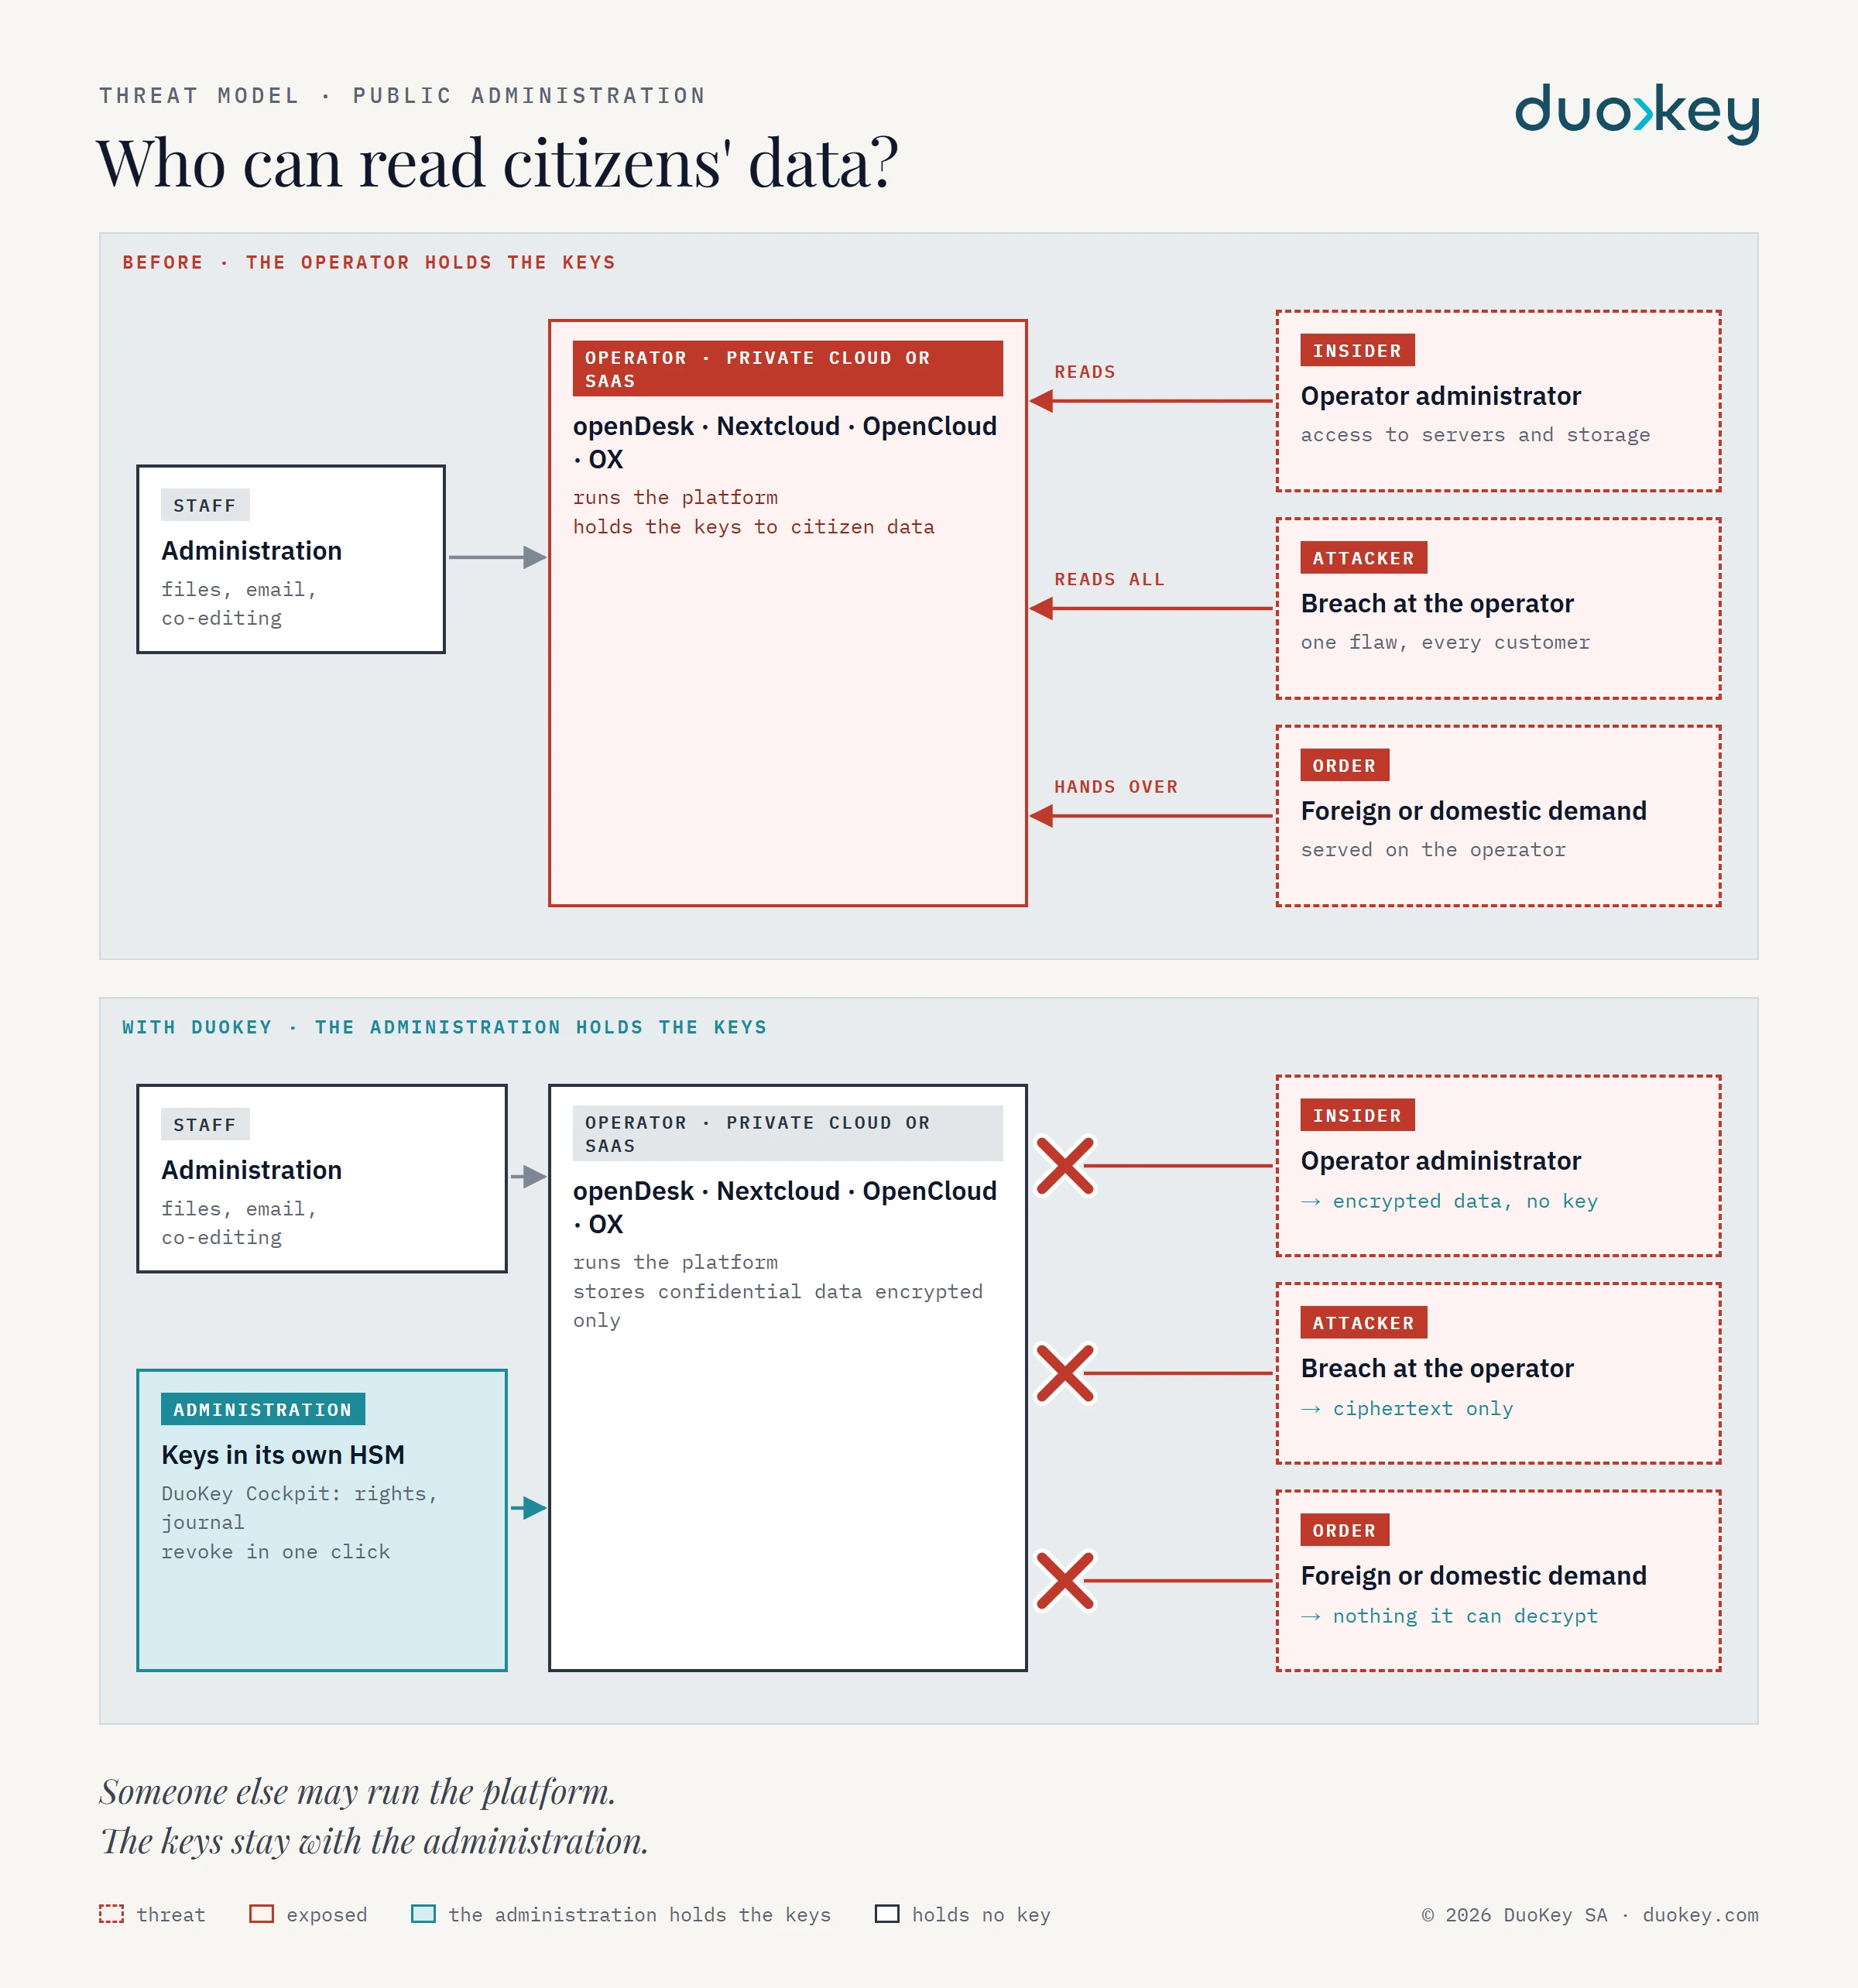
In a typical installation, as openDesk 1.20 ships it, mailboxes are stored unencrypted on the mail server's storage, and the OX Guard master key is a file in the cluster. Whoever runs, copies or takes over the server can therefore read. This is not a flaw in openDesk: a mail server has to deliver and display messages. The question is who holds the keys permanently.
How DuoKey Secure Open-Xchange works, simply explained
Three keys move out of the mail server into the DuoKey Cockpit, which the administration controls with its own HSM:
- The OX Guard master key is sealed and unsealed into memory only at start-up. If it is blocked in the Cockpit, Guard does not start.
- S/MIME from your own PKI. Certificates for encrypted email come from a DuoKey certificate authority. If a key is lost, it is recovered only under dual control.
- One key per mailbox. Every message is stored encrypted. The Cockpit releases the key per person and can withdraw it at any time.
Nothing changes for staff: they work in the same webmail.
What it means for your obligations
- Appropriate security. GDPR Article 32 names encryption explicitly; the Swiss FADP requires data security appropriate to the risk in Article 8.
- Providers. If someone runs the mail server for you, you remain responsible (GDPR Art. 28, FADP Art. 9). An operator that cannot read the mailboxes is a smaller risk.
- Data breaches. If copied mailboxes were encrypted and the key was not affected, notifying the people concerned can be waived under GDPR Article 34(3).
- After an incident. Instead of hoping an attacker read nothing, you withdraw the mailbox key in the Cockpit. The journal shows every release and every refusal.
- S/MIME keys. Issuance, escrow and recovery are governed and traceable, instead of improvised per person.
No product makes an administration compliant on its own. Secure Open-Xchange gives you measures you can evidence.
The limits, stated plainly
Mailbox encryption protects stored messages; when a person reads, the mail server decrypts with that person's released key. Only S/MIME is end to end between sender and recipient. Senders, recipients and subjects are visible to mail delivery, as with any email.
Test it
You run openDesk or OX App Suite? Test DuoKey Secure Open-Xchange with us in your environment, level by level.
Sources
- General Data Protection Regulation (EU) 2016/679, Articles 28, 32 and 34. eur-lex.europa.eu
- Swiss Federal Act on Data Protection (FADP), Articles 8 and 9. fedlex.admin.ch