Product demo
SecureFolder in 57 seconds
Real lab footage: openDesk CE 1.20, Nextcloud 33, Collabora Online 26.04. German version; English version coming.
Under your control: every folder key
SecureFolder takes encryption out of Nextcloud without taking browser work away from your teams.
No plaintext on the server
In protected folders, Nextcloud stores ciphertext only and holds no key.
Two independent checks
The share in Nextcloud and the key right in the Cockpit, run by two teams.
Keep co-editing
Collabora Online stays the editor: several people, at the same time, in the browser.
DuoKey SecureFolder · Platform
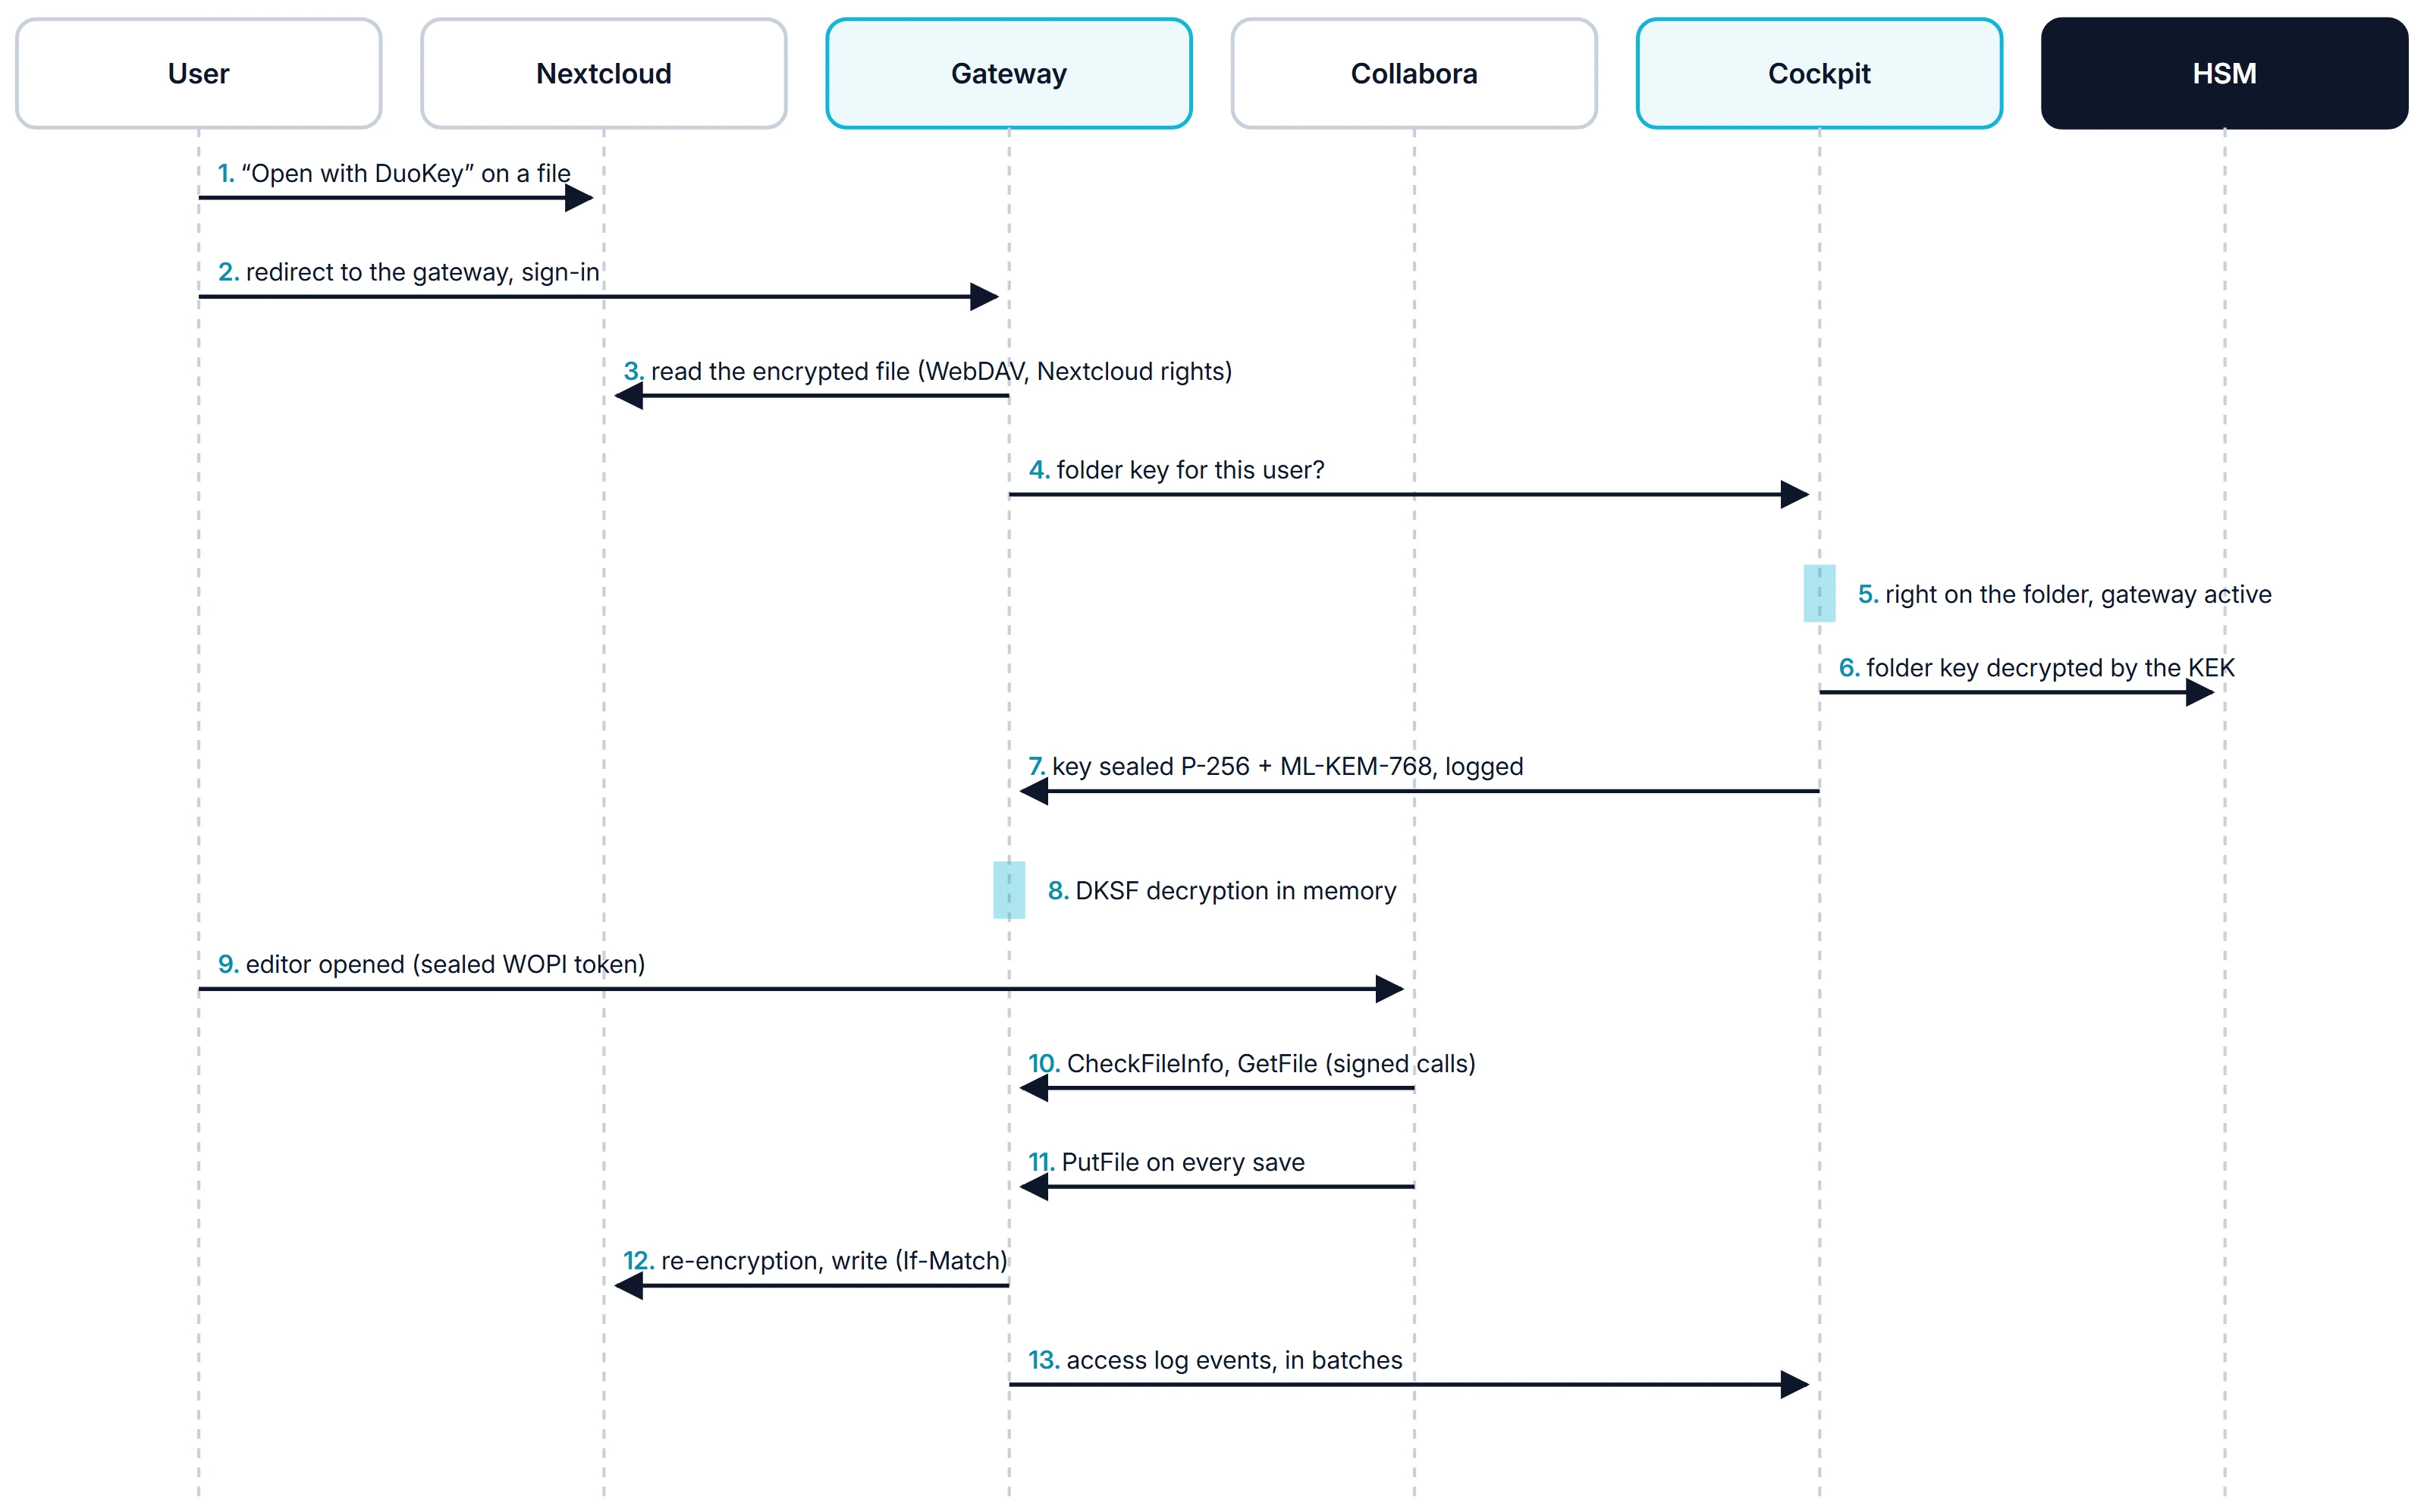
From “Open with DuoKey” to encrypted save
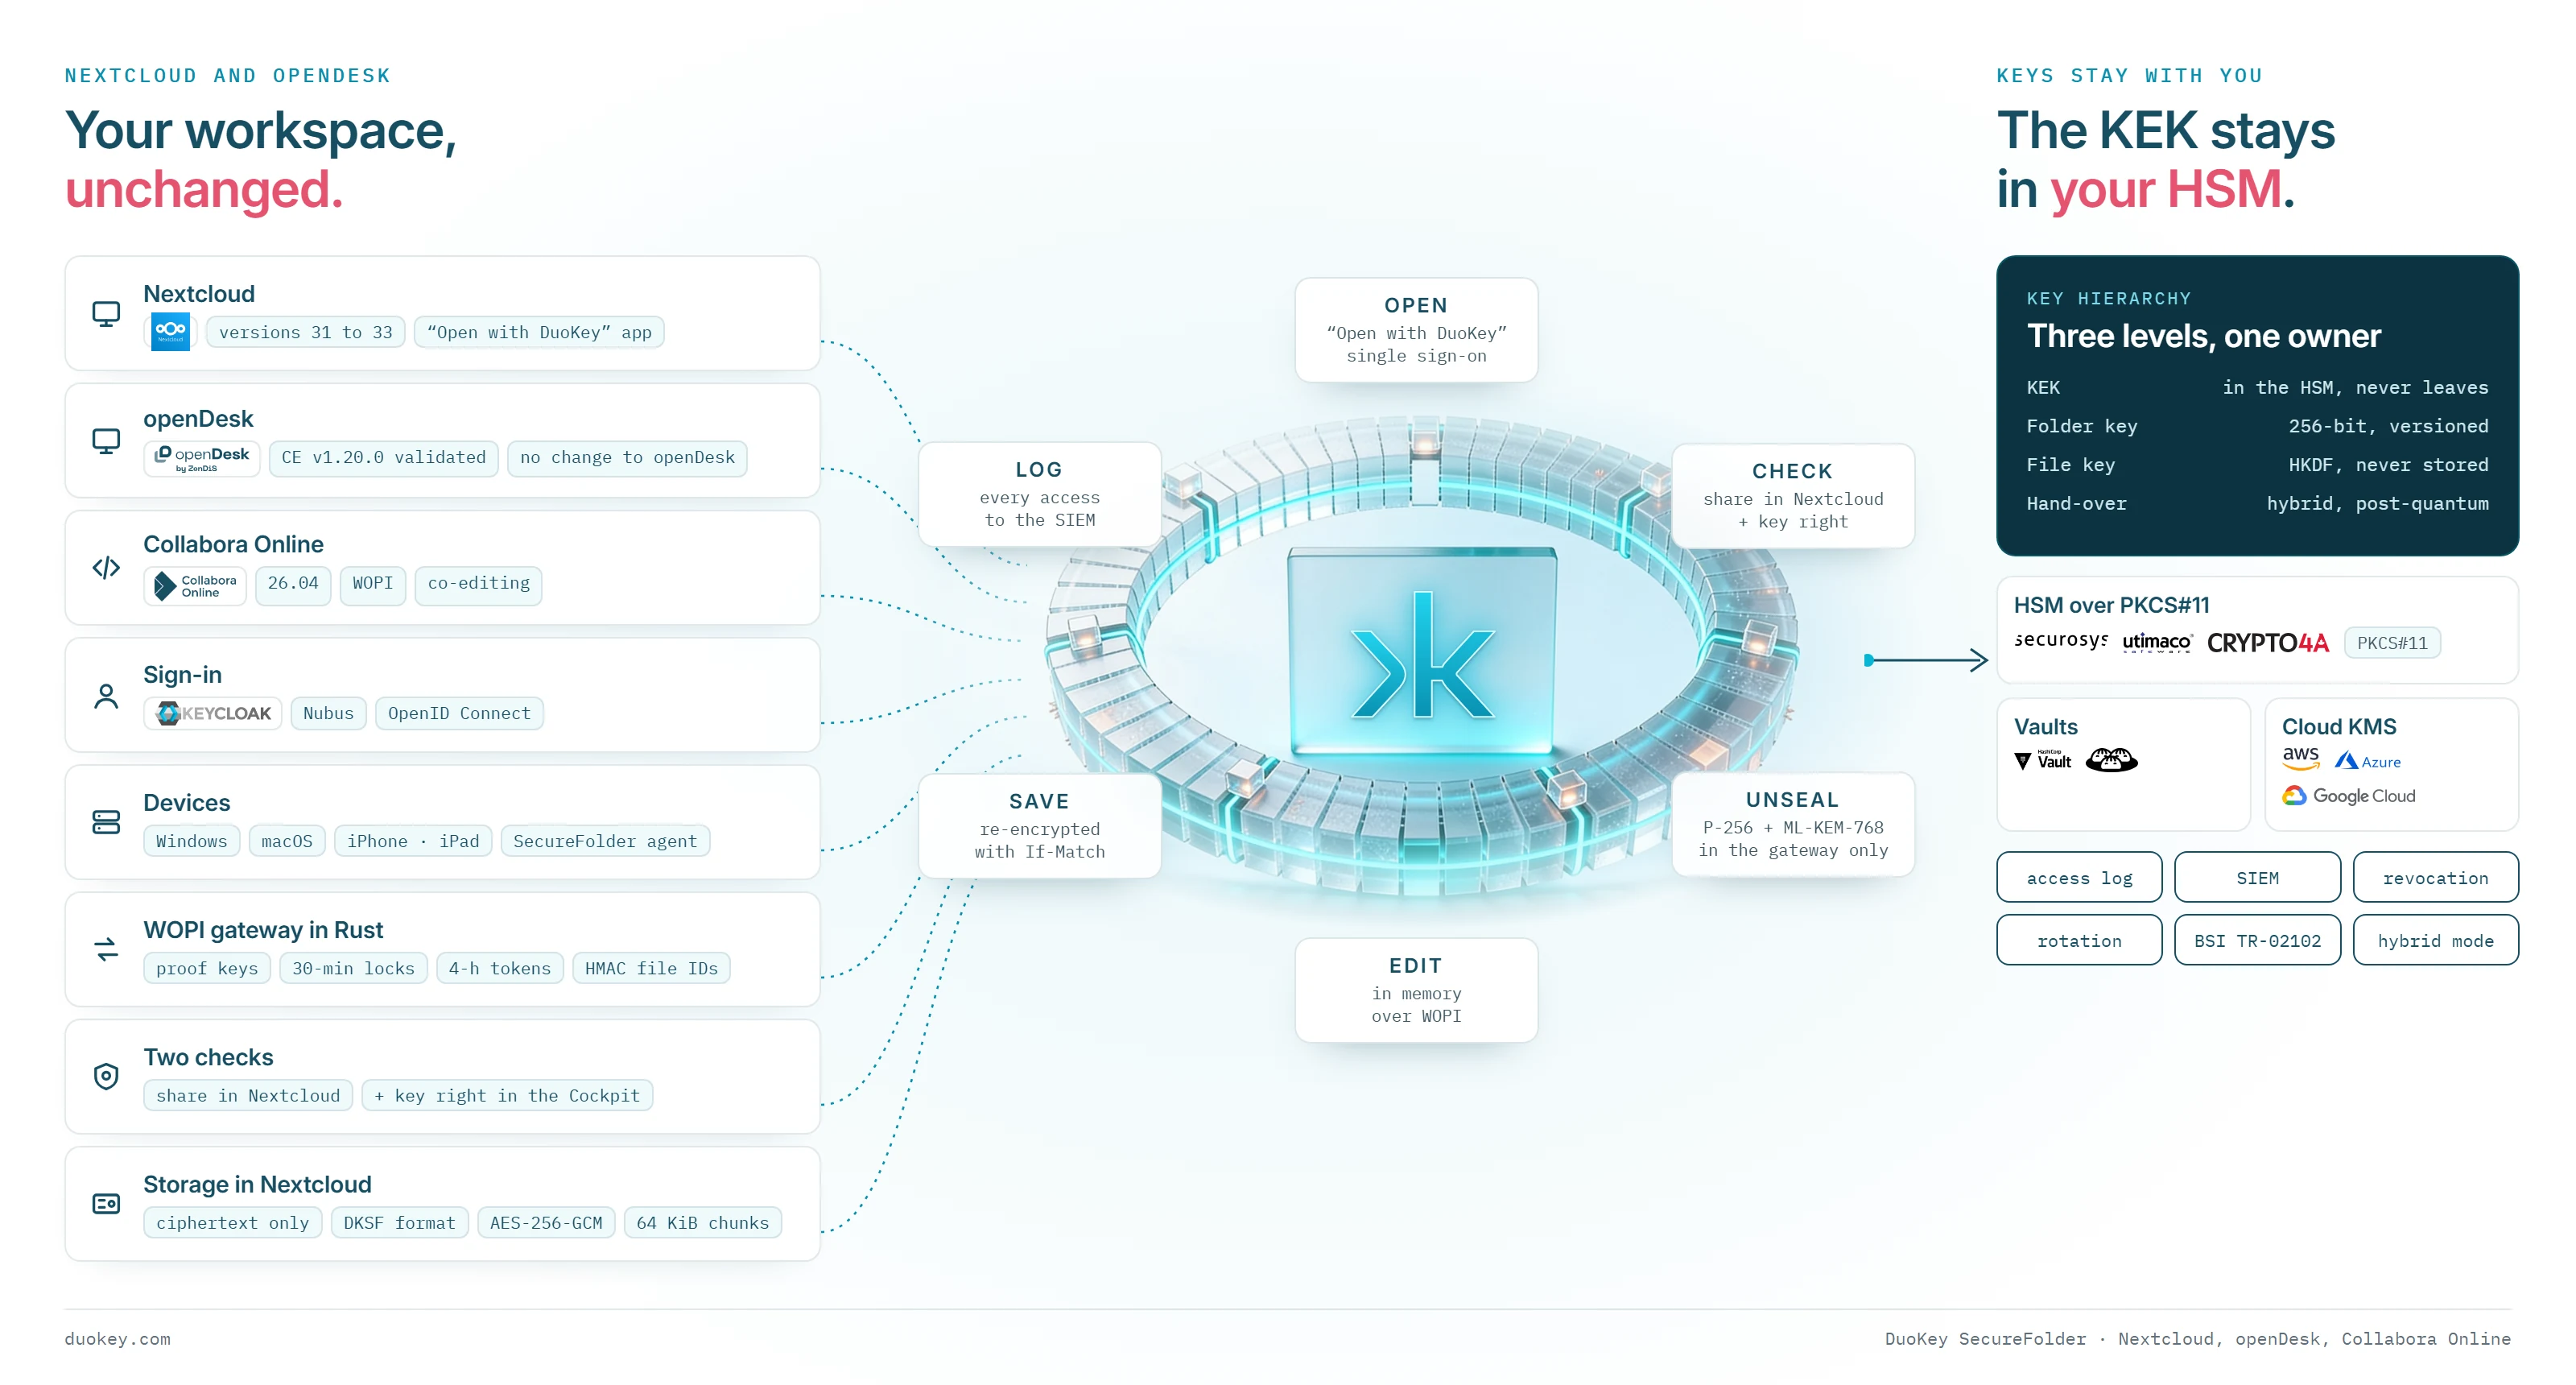
Nextcloud, openDesk and Collabora Online stay as they are. The DuoKey gateway opens, checks, unseals, hands the document to the editor and re-encrypts every save; the master key stays in your HSM.
Nextcloud sees ciphertext only.
Documents in protected folders are encrypted in the DKSF format with AES-256-GCM in 64 KiB chunks. A compromised server or a curious administrator finds no readable content and no key.
- The DuoKey app in Nextcloud holds no key itself.
- Names, sizes and shares stay visible; file name encryption is planned.
Two checks before a document opens.
Nextcloud checks the share, the DuoKey Cockpit checks the right to the folder key. If either is missing, the document stays closed, even for a Nextcloud administrator.
- Two teams, two consoles: separation of roles by design.
- No key right in the Cockpit, no document.
The master key never leaves your HSM.
The KEK sits in your organization's HSM or vault. Each folder has its own versioned key, wrapped by the KEK; file keys are derived and never stored.
- Generic PKCS#11, Securosys, Utimaco, Crypto4A, Vault, OpenBao and cloud KMS.
- Hand-over to devices and the gateway is hybrid-sealed: P-256 + ML-KEM-768.
Every access is on record.
Opens, saves, key releases and refusals go to the Cockpit access log and can be forwarded to your SIEM.
- Evidence per user, folder and key version.
- Records for NIS2, GDPR or ISO 27001 audits.
How it works
Encryption leaves Nextcloud, collaboration stays
A DuoKey gateway written in Rust sits between Nextcloud and Collabora Online as a WOPI host. It fetches the folder key from the Cockpit for an authorized user, decrypts in memory and re-encrypts on every save. On devices, the SecureFolder agent does the same for local applications.
- 01Open with DuoKey: a new menu entry in Nextcloud or openDesk
- 02Single sign-on over OpenID Connect, for example with openDesk's Keycloak
- 03Two checks: the share in Nextcloud and the key right in the Cockpit
- 04The gateway unseals the folder key and decrypts in memory only
- 05Collabora Online edits over WOPI, several people at the same time
- 06Every save is re-encrypted and stored in Nextcloud as ciphertext
Keys and post-quantum
Hybrid sealing, per BSI TR-02102-1
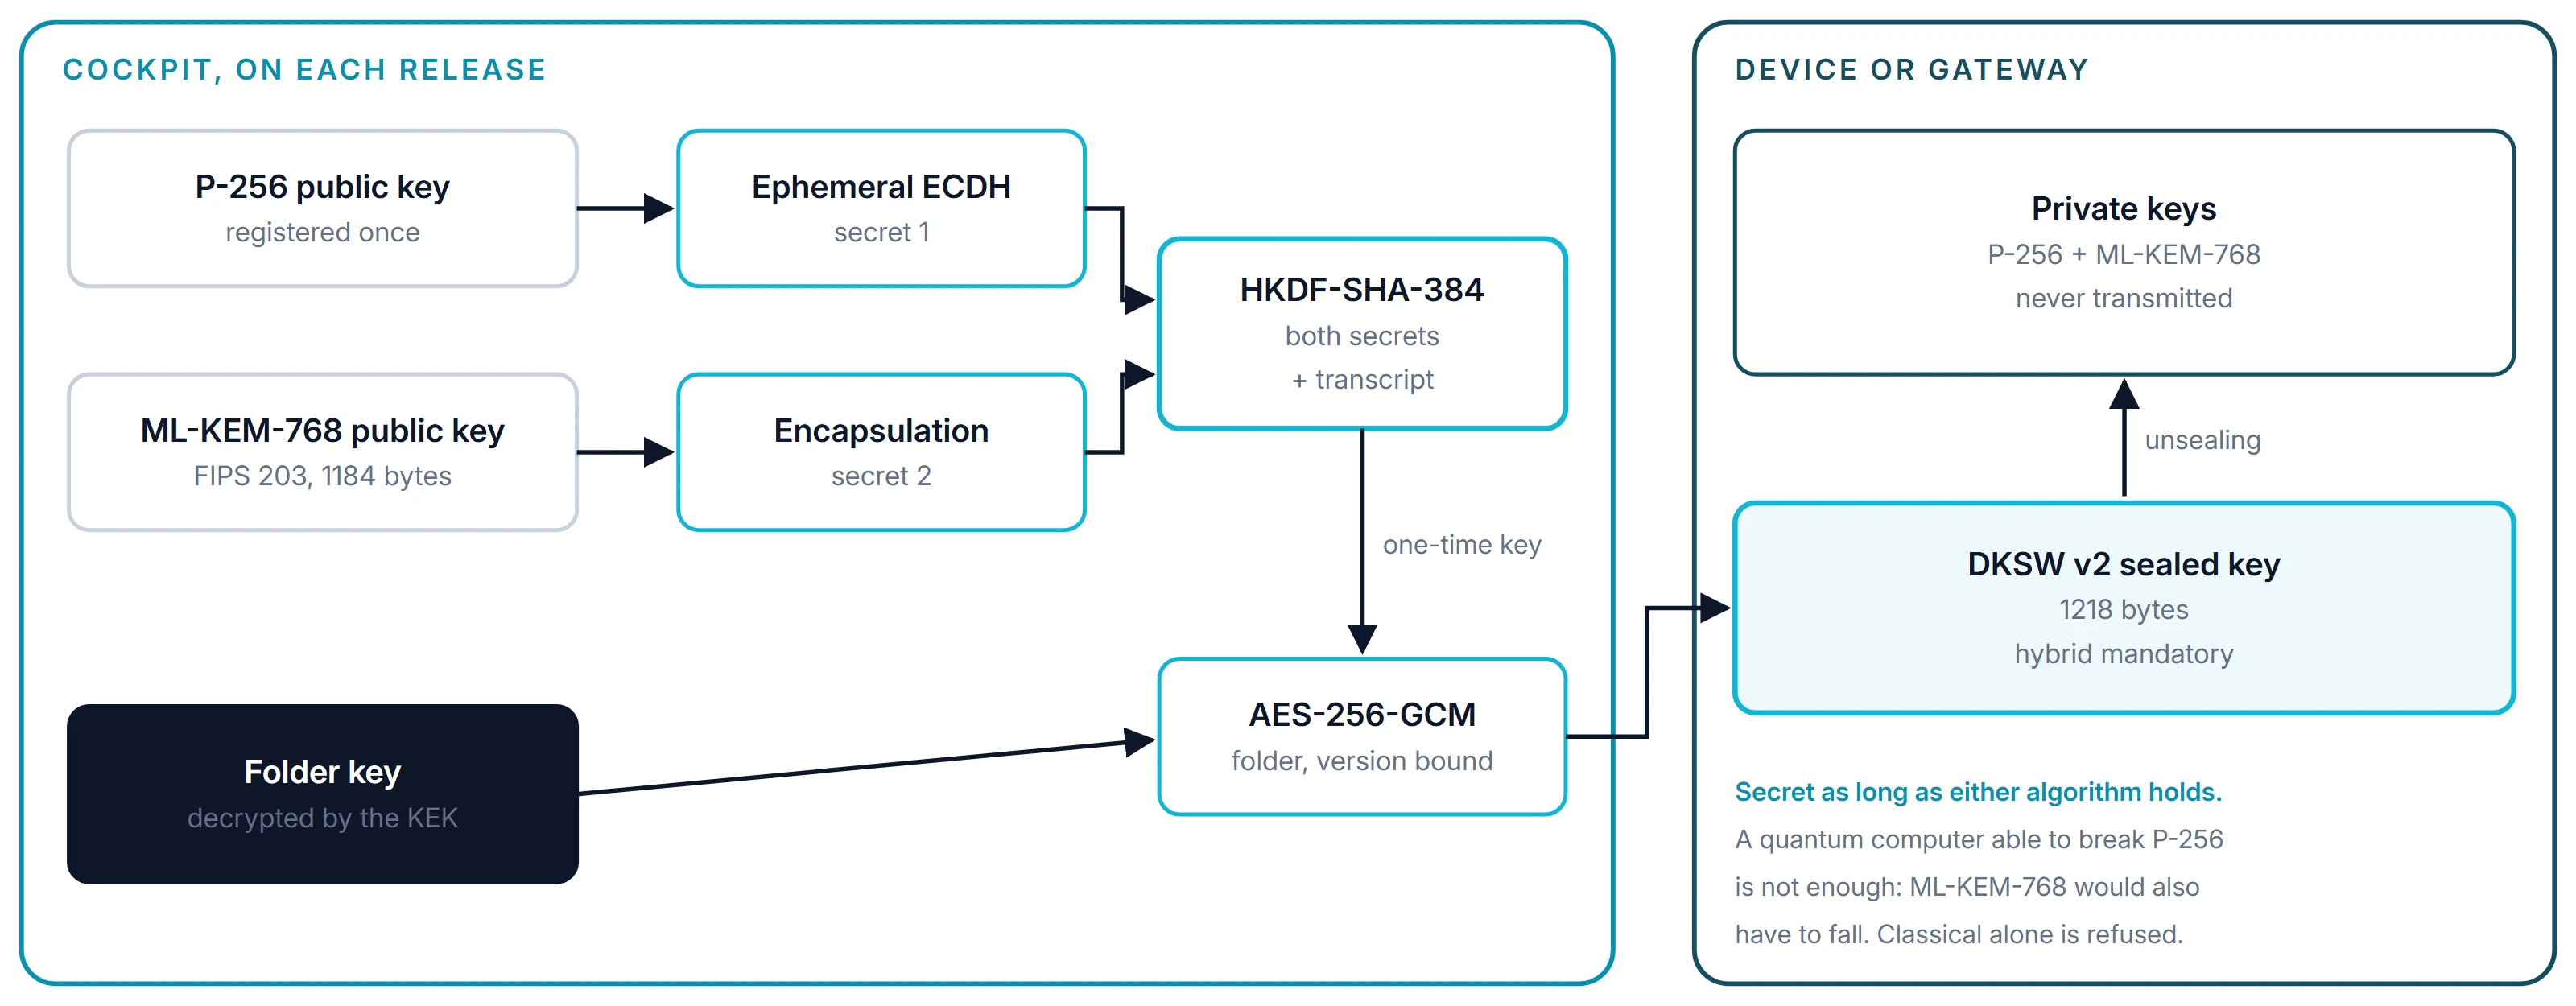
Every hand-over of a folder key to a device or to the gateway is sealed with P-256 and ML-KEM-768. The derived key stays secret as long as either scheme holds, as the German BSI has recommended for long-term confidentiality since version 2026-01 of TR-02102-1.
- KEK in the HSM or vault, it never leaves
- Folder key: 256-bit, versioned, wrapped by the KEK
- File keys derived with HKDF-SHA256, never stored
- The gateway rejects any non-hybrid sealing: no fallback to P-256 alone
Fits your openDesk environment
SecureFolder was validated on openDesk Community Edition v1.20.0, through its official customization points and without changing openDesk.
- Sign-in through openDesk's Keycloak (OpenID Connect)
- WOPI host for Collabora Online 26.04; OnlyOffice partial
- Access log forwarded to the SIEM
Comparison
Community, Enterprise and SecureFolder
SecureFolder replaces neither Nextcloud Enterprise nor openDesk Enterprise; it complements them. An Enterprise subscription lowers the likelihood of a compromise; SecureFolder limits its consequences.
Nextcloud editions
| Community, server-side | Enterprise, server-side | Nextcloud end-to-end | With SecureFolder | |
|---|---|---|---|---|
| Where the key sits | On the server, protected by an instance secret (master key mode by default) | Same | On users' devices | KEK in your organization's HSM |
| The server administrator can decrypt | Yes, in master key mode [1] | Yes | No | No |
| Compromised server | Documents exposed [1] | Documents exposed | Ciphertext only | Ciphertext only |
| Co-editing in the browser | Yes | Yes | No: since Hub 10, browse and download only in the browser [2] | Yes, through the gateway |
| File names, previews, search index | Not encrypted [3] | Not encrypted | Names encrypted | Names in clear (encryption planned); no previews, no index |
| Security fixes | Major version maintained for one year [4] | Early fixes, 5 to 10 years of support [5] | Depends on the edition | Independent of Nextcloud |
| Log of every key release and every open | No | No | No | Yes, forwarded to the SIEM |
openDesk editions
| openDesk Community | openDesk Enterprise | openDesk with SecureFolder | |
|---|---|---|---|
| Publisher | ZenDiS, on behalf of the German Federal Ministry of the Interior [6] | ZenDiS | ZenDiS and DuoKey |
| File and office components | Nextcloud 33 and Collabora Online 26.04 [6] | Same | Same: the versions the gateway is validated on |
| Support | Community, no service commitment [7] | Support with SLA, 2nd and 3rd level [7] | DuoKey support for SecureFolder |
| Customer-held keys for files | Not mentioned in the public documentation [8] | Not mentioned in the public documentation | Yes: KEK in the organization's HSM |
| Co-editing of encrypted documents | Not documented | Not documented | Yes |
- [1] Nextcloud, administration manual: server-side encryption: docs.nextcloud.com/server/latest/admin_manual/configuration_files/encryption_configuration.html
- [2] Nextcloud Hub 10 announcement (end-to-end encryption in the browser): help.nextcloud.com/t/nextcloud-hub-10-your-unified-modular-digital-workspace/218337
- [3] Nextcloud, server-side encryption details: docs.nextcloud.com/server/latest/admin_manual/configuration_files/encryption_details.html
- [4] Nextcloud, release schedule: docs.nextcloud.com/server/stable/admin_manual/release_schedule.html
- [5] Nextcloud Enterprise: nextcloud.com/enterprise/
- [6] openDesk, operations documentation: components: docs.opendesk.eu/operations/introduction
- [7] openDesk, Enterprise Edition: docs.opendesk.eu/operations/enterprise/
- [8] openDesk, frequently asked questions: www.opendesk.eu/en/faq
Sources checked 8 to 10 November 2026.
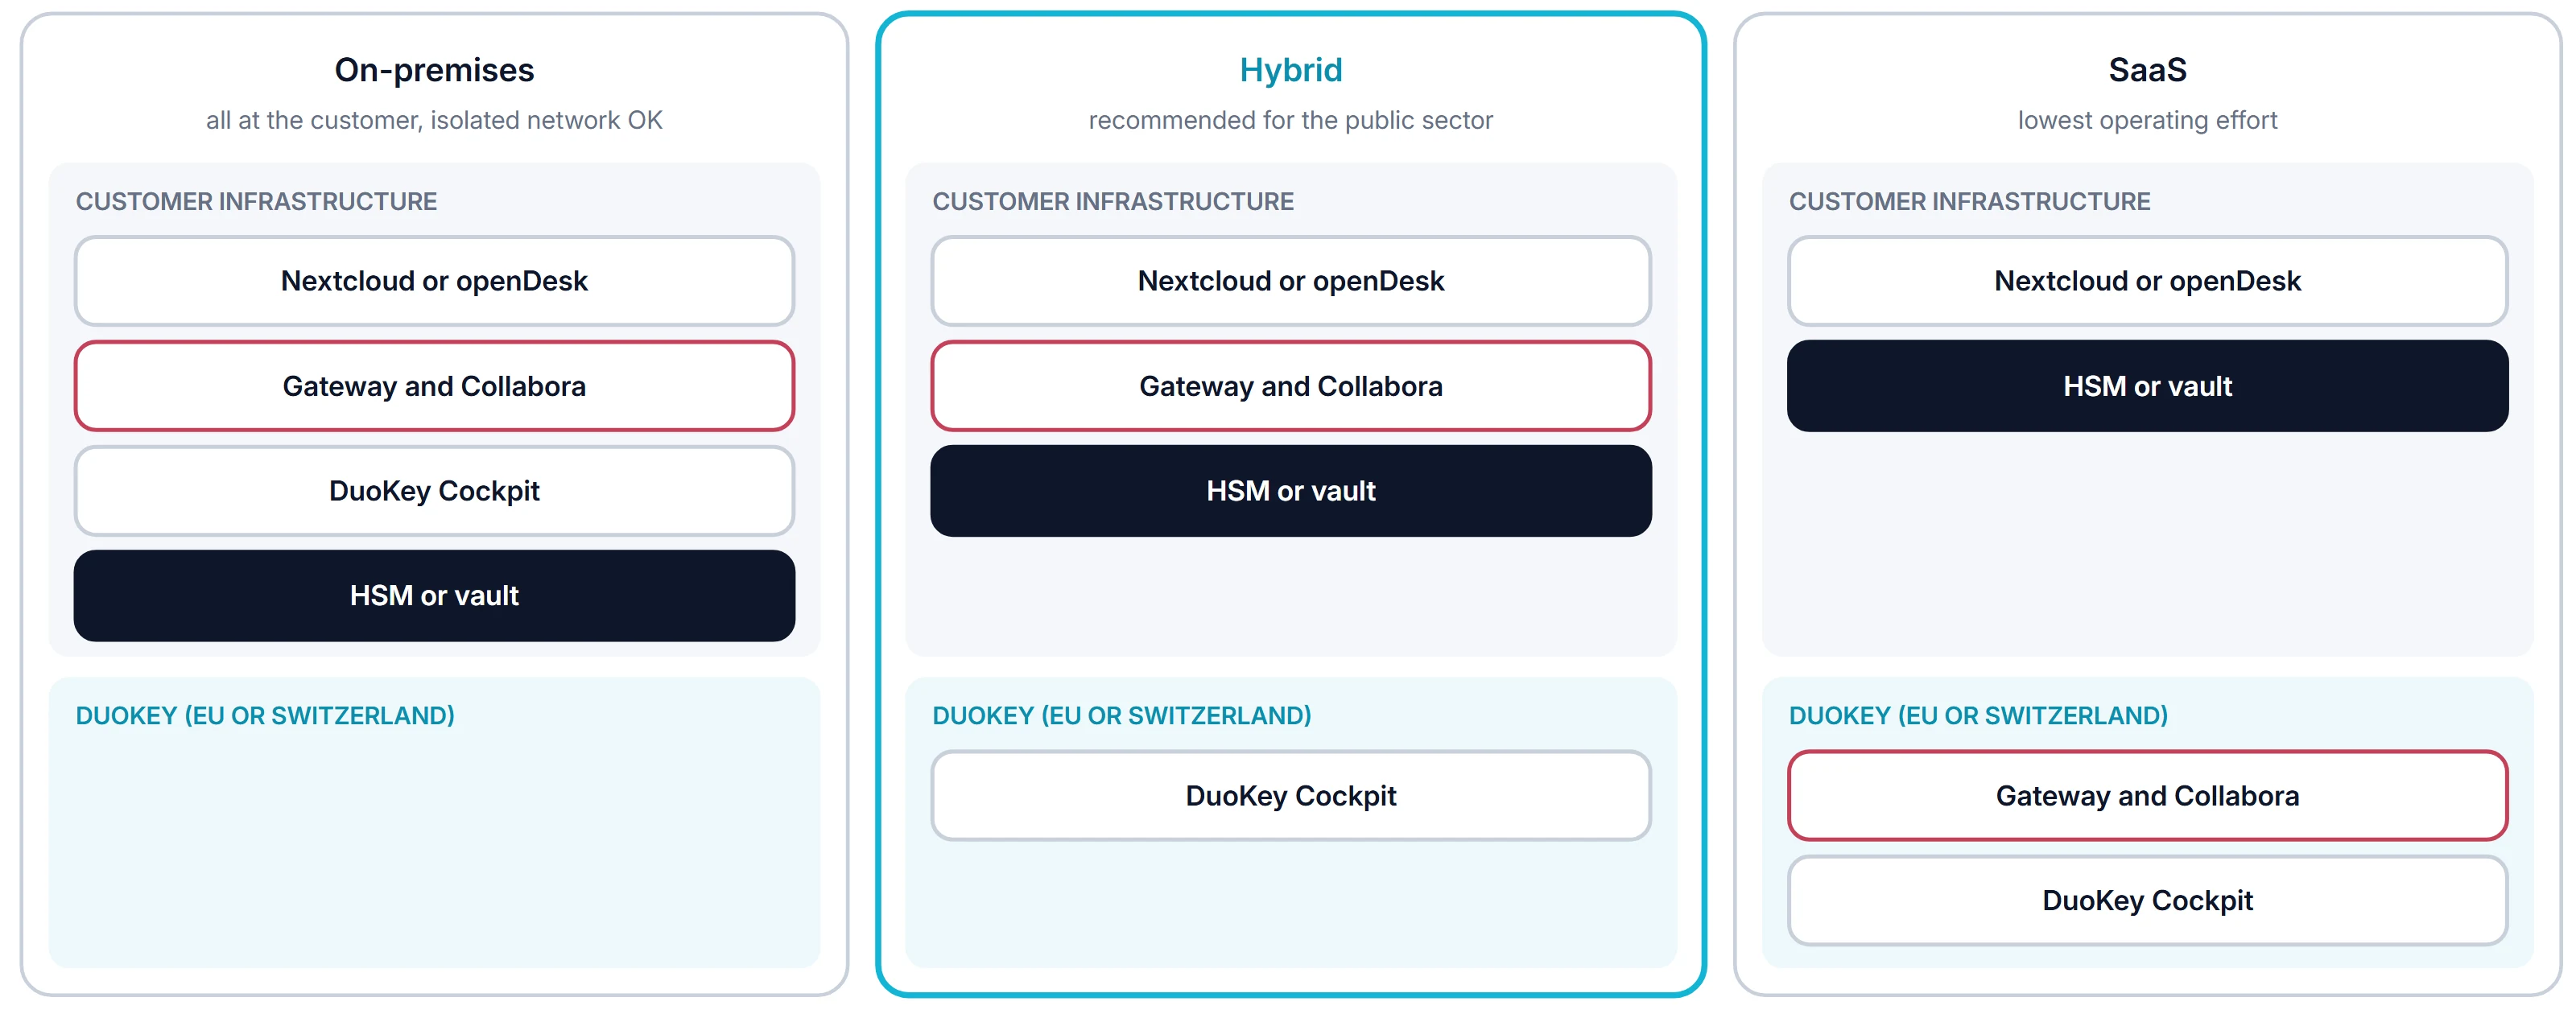
On premises, hybrid or as a service
On premises and in hybrid mode, DuoKey does not hold your master keys. For every feature we state where it stands.
| Feature | Status | Note |
|---|---|---|
| DKSF file format, key hierarchy, hybrid sealing P-256 + ML-KEM-768 | Implemented | Rust library shared by agent and gateway |
| WOPI gateway with Collabora Online: open, co-edit, encrypted save | Implemented | Validated on Nextcloud 33 and Collabora Online 26.04 |
| Nextcloud app “Open with DuoKey” | Implemented | Nextcloud 31 to 33 |
| openDesk | Validated | openDesk CE v1.20.0, without changing openDesk |
| Access log in the Cockpit, forwarding to the SIEM | Implemented | |
| SecureFolder agent for Windows and macOS, app for iPhone and iPad | Implemented | |
| OnlyOffice Docs | Partial | Compatible protocol, full validation pending |
| SaaS editing zone per customer in a hardware enclave | Planned | Demo environment in progress |
| Hosting in Switzerland | Planned | With a Swiss provider or in hybrid mode |
Status: November 2026, per the SecureFolder security whitepaper v1.2.
Deep dives
Field guides for your programme
FAQ
SecureFolder, frequently asked questions
SecureFolder keeps the documents of a folder in Nextcloud or openDesk encrypted. The master keys stay in your organization's HSM or vault, and your teams keep co-editing documents in the browser with Collabora Online.
No. In protected folders, Nextcloud stores only ciphertext in the DKSF format and holds no key. The DuoKey Cockpit releases the folder key only to a user who has the right to it; a Nextcloud share alone is not enough.
Yes. The DuoKey gateway is a WOPI host: Collabora Online opens and saves the document through the gateway, which decrypts in memory and re-encrypts on every save. Several people edit the same document at the same time.
No. SecureFolder was validated on openDesk Community Edition v1.20.0 (Nextcloud 33, Collabora Online 26.04, Nubus), through its official customization points and without changing openDesk. Sign-in goes through openDesk's Keycloak.
The hand-over of folder keys to devices and to the gateway is hybrid-sealed with P-256 and ML-KEM-768, following the recommendation of BSI TR-02102-1 (version 2026-01). File content is encrypted with AES-256-GCM.
The Cockpit uses its existing connectors: generic PKCS#11, Securosys, Utimaco, Crypto4A, DuoKey HSM, HashiCorp Vault, OpenBao, Azure Key Vault, AWS KMS and Google Cloud KMS. An HSM approved in your country can be used over PKCS#11.
File names, sizes, dates and shares, but not the content. File name encryption is planned. Protected folders have no previews and no search index.
Your documents in openDesk. Your keys with you.
We show you SecureFolder with Nextcloud, openDesk and Collabora Online, in your own test environment if you wish.